Skip to content

Cybersecurity & Compliance Consulting

Break the barriers in cyber threats. Build resilience in your systems.

TIRAM provides end-to-end consulting, auditing, advisory and training for ISO/IEC 27001, ISO/IEC 27701, ISO/IEC 20000-1, ISO/IEC 42001, ISO 22301, TISAX and SOC 1 & SOC 2 — helping small and medium sized companies achieve and sustain compliance.

20+
years in Information Security
7
standards
4
sectors

One accountable partner — the same proven path for every standard we deliver.

Why engage TIRAM

Two ways to get certified.

The same standards, the same audit at the end — the difference is the path. Drag the divider to compare going it alone with an expert-led engagement.

  1. 1
    Your companyISO/IEC 27001 · ISO/IEC 27701 · ISO/IEC 20000-1 · ISO/IEC 42001 · ISO 22301 · TISAX · SOC 1 & SOC 2
  2. 2
    Engage TIRAMOne accountable partner for the whole journey
  3. 3
    Gap assessment
  4. 4
    Policy & implementation
  5. 5
    Training
  6. 6
    Internal audit
  7. 7
    Certification audit
  8. ✓
    Audit success — certified

What We Do For You

Our Services

Four service lines covering the full compliance lifecycle — from gap assessment through implementation, audit and certification readiness.

Industries

Industry-acclaimed expertise

Our specialization includes Automotive, Financial, Healthcare and Software companies, with industry acclaimed certifications.

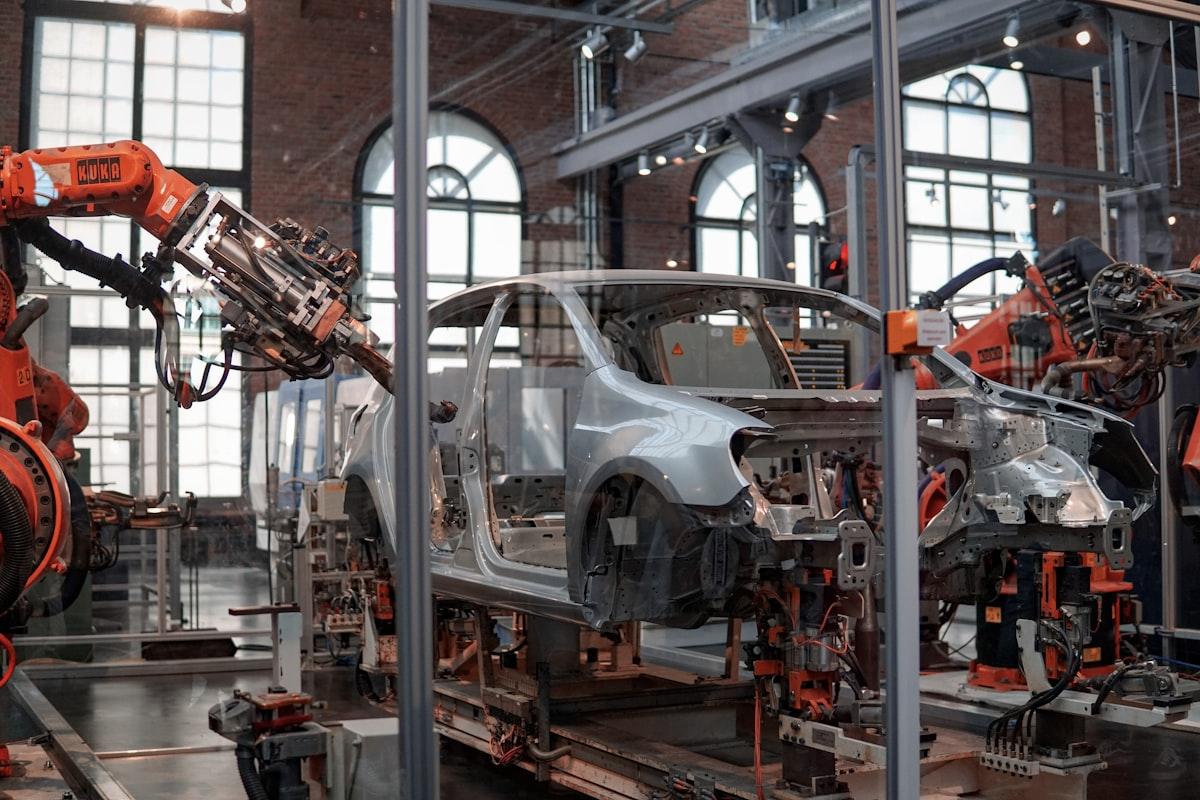
Robotic automotive assembly lineAutomotive

Automotive

TISAX and information security assurance for manufacturers and tier suppliers.

TISAXISO/IEC 27001Supplier audits
Explore Automotive

Contact Us

Get In Touch

Tell us about your compliance goals and we will come back to you with a clear scope, effort and timeline — no obligation.